In Brief: Cryptography in Cybersecurity
Encryption makes readable information inaccessible without the appropriate key. Hashing creates a fixed-length digest and is not designed to be reversed like encryption. Digital certificates connect identities with public keys through a trusted certificate system. TLS uses cryptography to help protect data moving between clients and servers.
Every time someone signs in to a secure website, sends sensitive information online, or connects to a protected service, cryptography may be working behind the scenes.
Cryptography in cybersecurity uses mathematical techniques to help protect information from unauthorized access or modification and to support authentication and integrity. Encryption, hashing, digital certificates, keys, and TLS perform different jobs, but modern security systems often use them together.
For students in our Applied Cybersecurity Engineer Diploma Program, understanding these relationships provides an important foundation for network, identity, and information security.
What Is Cryptography in Cybersecurity?
Cryptography is the use of techniques that transform or process information to provide security properties such as confidentiality, integrity, and authentication. Encryption is one familiar example. The Canadian Centre for Cyber Security explains that encryption encodes information so unauthorized people cannot read it without the appropriate key.
But cryptography extends beyond keeping information secret. It also supports digital signatures, key establishment, message authentication, hashing, certificates, and secure network protocols.
This is why encryption and key management need to be considered together. Strong encryption still depends on keys being generated, stored, distributed, rotated, and protected appropriately. The Cyber Centre describes cryptographic keys and secrets as critical organizational assets requiring protection throughout their lifecycle.
What Is the Difference Between Encryption and Hashing?
Encryption transforms readable data into ciphertext that an authorized party can decrypt with the appropriate key, while hashing transforms input into a fixed-length digest and is designed as a one-way process.
The distinction is important.
Encryption:
Plaintext → encryption + key → ciphertext → decryption + key → plaintext
Hashing:
Input → hash function → fixed-length digest
The Cyber Centre defines a hash function as a procedure that transforms a message of arbitrary length into a fixed-length digest. Secure cryptographic hash functions are designed to provide properties such as collision resistance, making it computationally infeasible to find different messages that produce the same digest.
Hashes can therefore support integrity checking, digital signatures, and message authentication. They are not simply another form of encryption.
A Digital Certificate and How It Works
A digital certificate is a digitally signed document that binds an identity to a public key. The Cyber Centre defines a public-key certificate as a digital document issued and digitally signed by a certificate authority (CA), connecting the subscriber’s identity with a public key.
When your browser connects to an HTTPS website, certificates form part of the process used to authenticate the server. The client can check whether the certificate chains back to a trusted CA and whether it meets relevant validation requirements.
For students learning about digital certificates in cybersecurity, this introduces an important concept: online trust is not based solely on encryption. Systems also need mechanisms for deciding which identities and keys should be trusted.
That relationship is closely tied to identity and access management in cybersecurity.
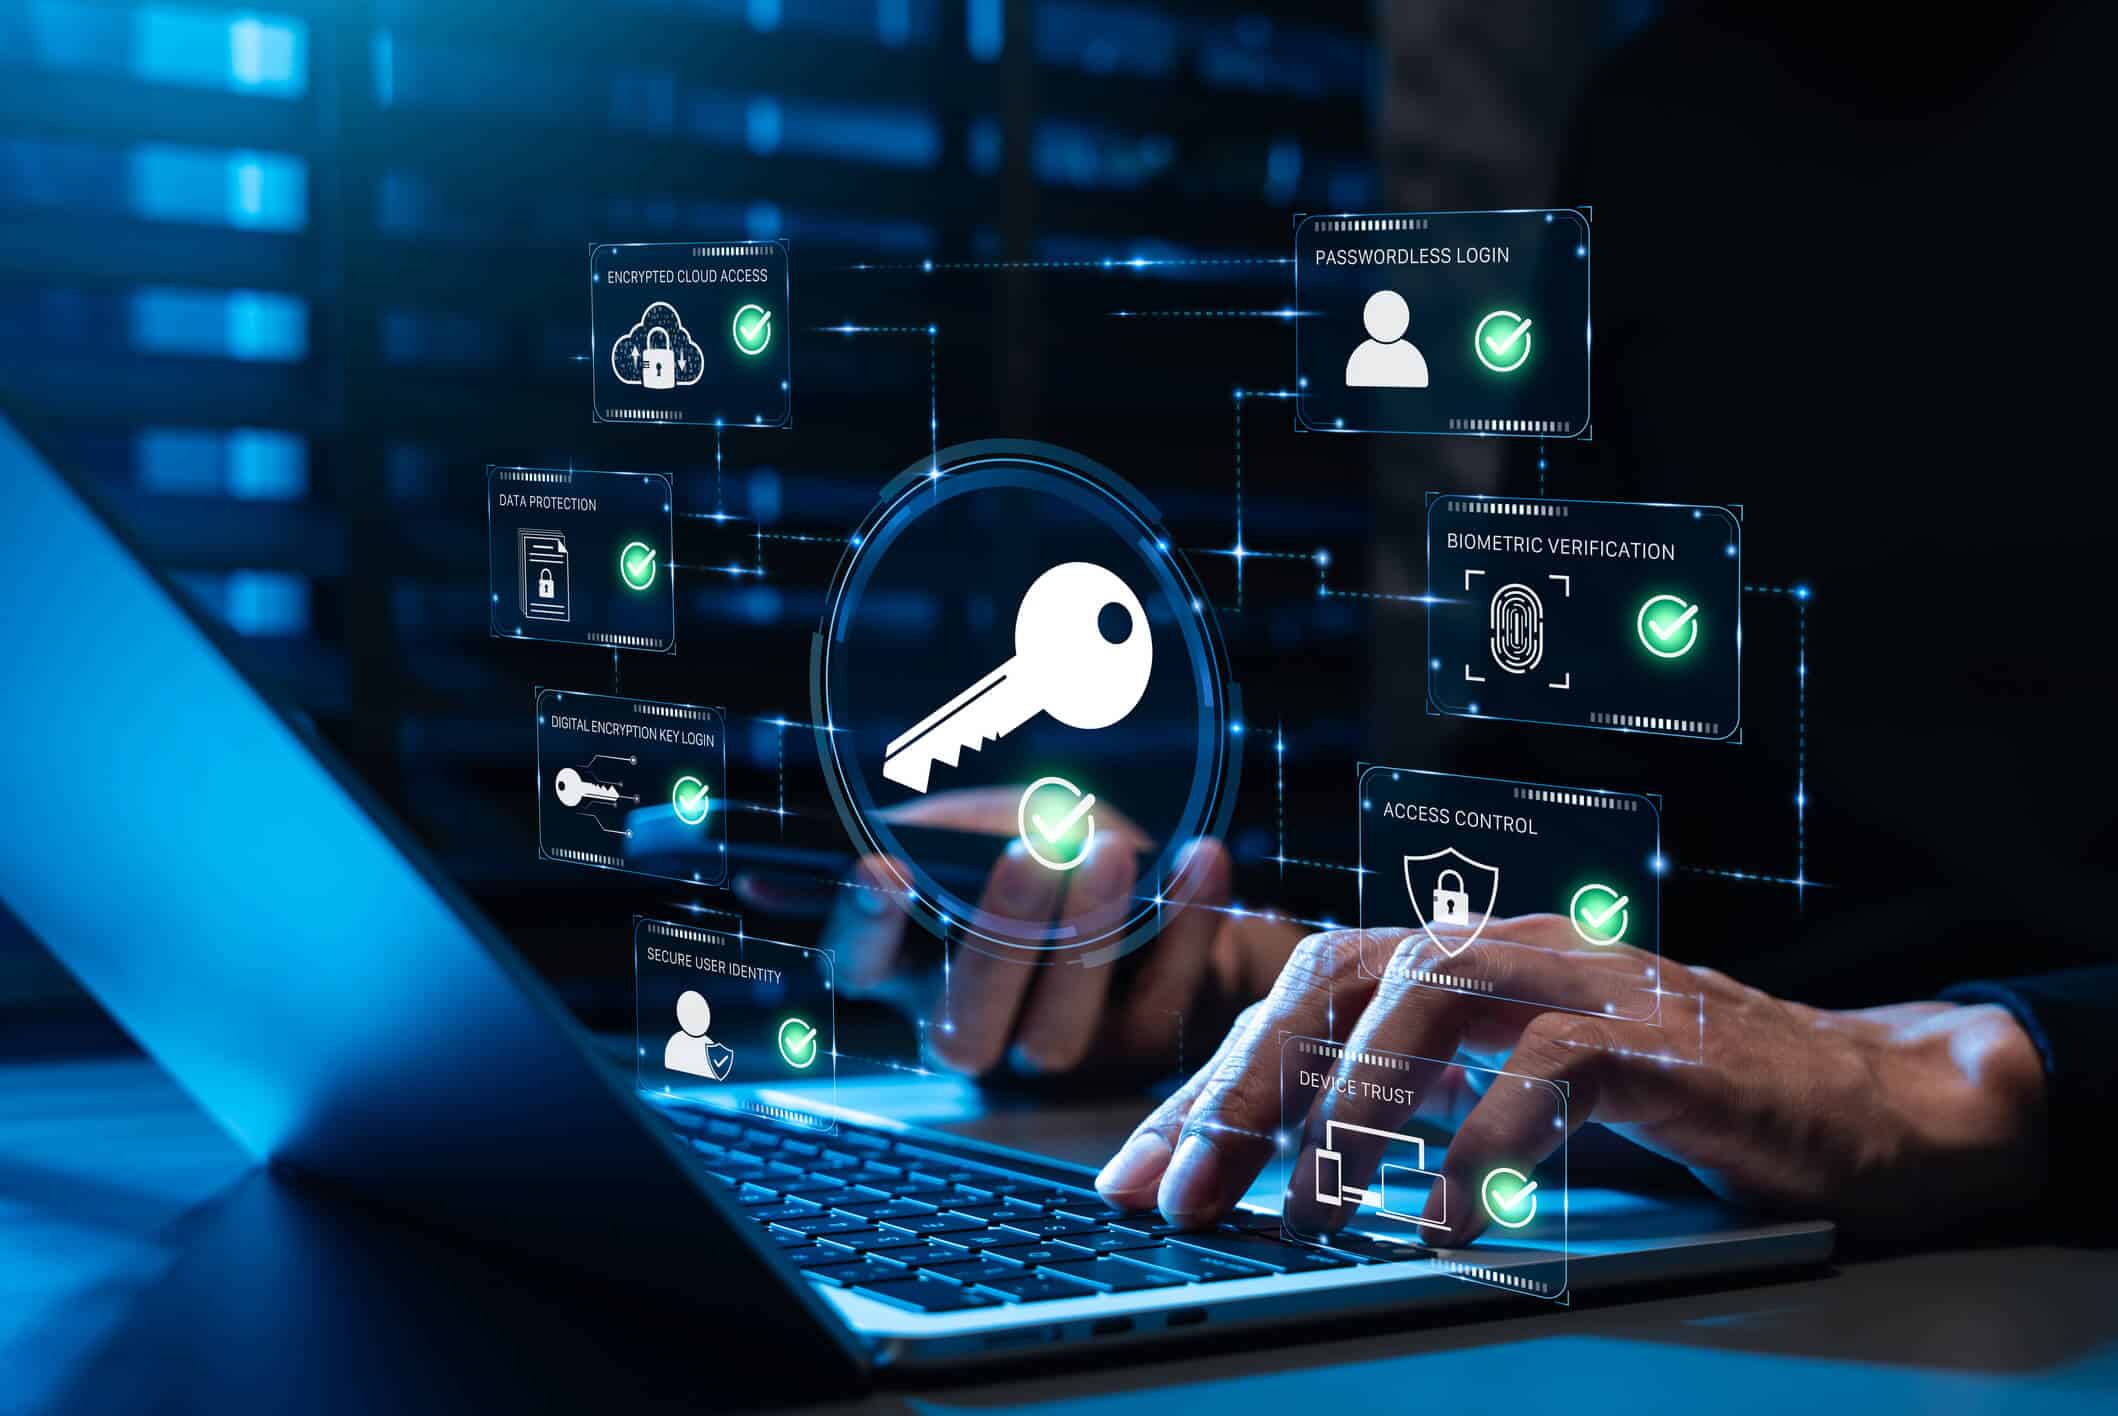
Public and private keys perform different but complementary functions in asymmetric cryptography
What Is Public Key Infrastructure?
Public key infrastructure, or PKI, is the collection of technologies, policies and processes used to administer digital certificates and public-private key pairs.
A PKI can involve certificate authorities, certificates, public and private keys, trust stores, certificate issuance, maintenance, validation and revocation. The Cyber Centre notes that PKIs support public-key management for security protocols including TLS, IPsec and S/MIME.
A simplified trust sequence looks like this:
Identity → certificate → public key → trusted CA → certificate validation
This is the foundation behind many PKI cybersecurity applications.
The Cyber Centre also recommends X.509 version 3 certificates for public-key certificates in the configurations covered by its network-protocol guidance.
Digital certificates connect identities with public keys through a trusted certificate system
What Is the Difference Between Public and Private Keys?
They are mathematically related parts of an asymmetric cryptographic key pair, but they have different functions.
A public key is designed to be shared. Depending on the cryptographic operation, it can be used to encrypt data or verify a digital signature.
A private key must remain secret. It can be used to decrypt appropriate data or create a digital signature. The Cyber Centre defines these roles similarly: public keys can verify signatures or encrypt data, while private keys can digitally sign or decrypt data.
Protecting the private key is critical. If an attacker obtains it, the security assumptions built around that key pair may be compromised.
TLS combines several cryptographic mechanisms to protect communications between applications
How TLS, Certificates, and Cryptography Work Together
TLS encryption demonstrates how several of these concepts combine in a real network protocol.
Transport Layer Security protects communications between client and server applications. The Cyber Centre states that TLS is designed to protect the confidentiality, integrity, and availability of Internet communications and currently recommends TLS 1.3, while TLS 1.2 can remain sufficient where compatibility or other requirements make it necessary. Versions older than TLS 1.2 and SSL should be phased out.
During a secure connection, TLS can use certificates and public-key cryptography for authentication and key establishment, then use efficient symmetric cryptography to protect session data.
That makes TLS a useful example for students studying network security and secure communications. Instead of viewing encryption, certificates, PKI, and keys as separate vocabulary terms, students can see how they contribute to a working security protocol.
Do you want to build practical knowledge of encryption, network security, authentication, and other technologies used to protect digital systems?
AAPS College’s Applied Cybersecurity Engineer Diploma Program gives students opportunities to develop cybersecurity skills through hands-on technical training.
Contact AAPS College to learn more about the program.
Key Takeaways
- Cryptography in cybersecurity supports confidentiality, integrity, authentication, and other security functions.
- Encryption and hashing serve different purposes and should not be treated as interchangeable.
- Digital certificates bind identities to public keys within a trust framework.
- Public key infrastructure manages certificates and public-private key pairs.
- Public keys can be shared, while private keys must be protected.
- TLS brings multiple cryptographic mechanisms together to secure network communications.
FAQ
What is cryptography in cybersecurity?
Cryptography in cybersecurity uses mathematical techniques to help protect information, verify integrity, authenticate entities, and support secure communications.
What is the difference between encryption and hashing?
Encryption transforms data so it can later be decrypted with an appropriate key. Hashing produces a fixed-length digest and is designed as a one-way process rather than a reversible form of encryption.
What is a digital certificate and how does it work?
A digital certificate is a digitally signed document that connects an identity with a public key. Certificate authorities and trust mechanisms allow systems to validate certificates before relying on them.
What is public key infrastructure?
Public key infrastructure is the combination of policies, processes, software, systems, certificates, and cryptographic keys used to administer public-key certificates and trust relationships.
What is the difference between public and private keys?
A public key can be distributed and used for operations such as encryption or signature verification. Its corresponding private key is kept secret and can perform complementary operations such as decryption or creating digital signatures.